6 Steps to Prepare Your Technology, Reduce Cyber Liability, and Protect Your Mission Before Year-End
There’s something impressive about the way families prepare for back-to-school season.
Backpacks get packed. Supplies are purchased. Bedtimes are adjusted. Transportation is planned.
In the middle of everything else happening at the end of summer, families take time to prepare for what comes next.
There’s a good lesson in that for nonprofit leaders.
A little preparation at the right time can change how the whole season goes.
The final months of the year can bring a lot at once: year-end giving, grant deadlines, board meetings, budget planning, program demands, staff vacations, and increased online activity.
Technology supports nearly every part of it.
Before calendars fill and everything starts feeling urgent, now is a good time to understand where your organization stands, identify what deserves attention, and build an informed plan for the months ahead.
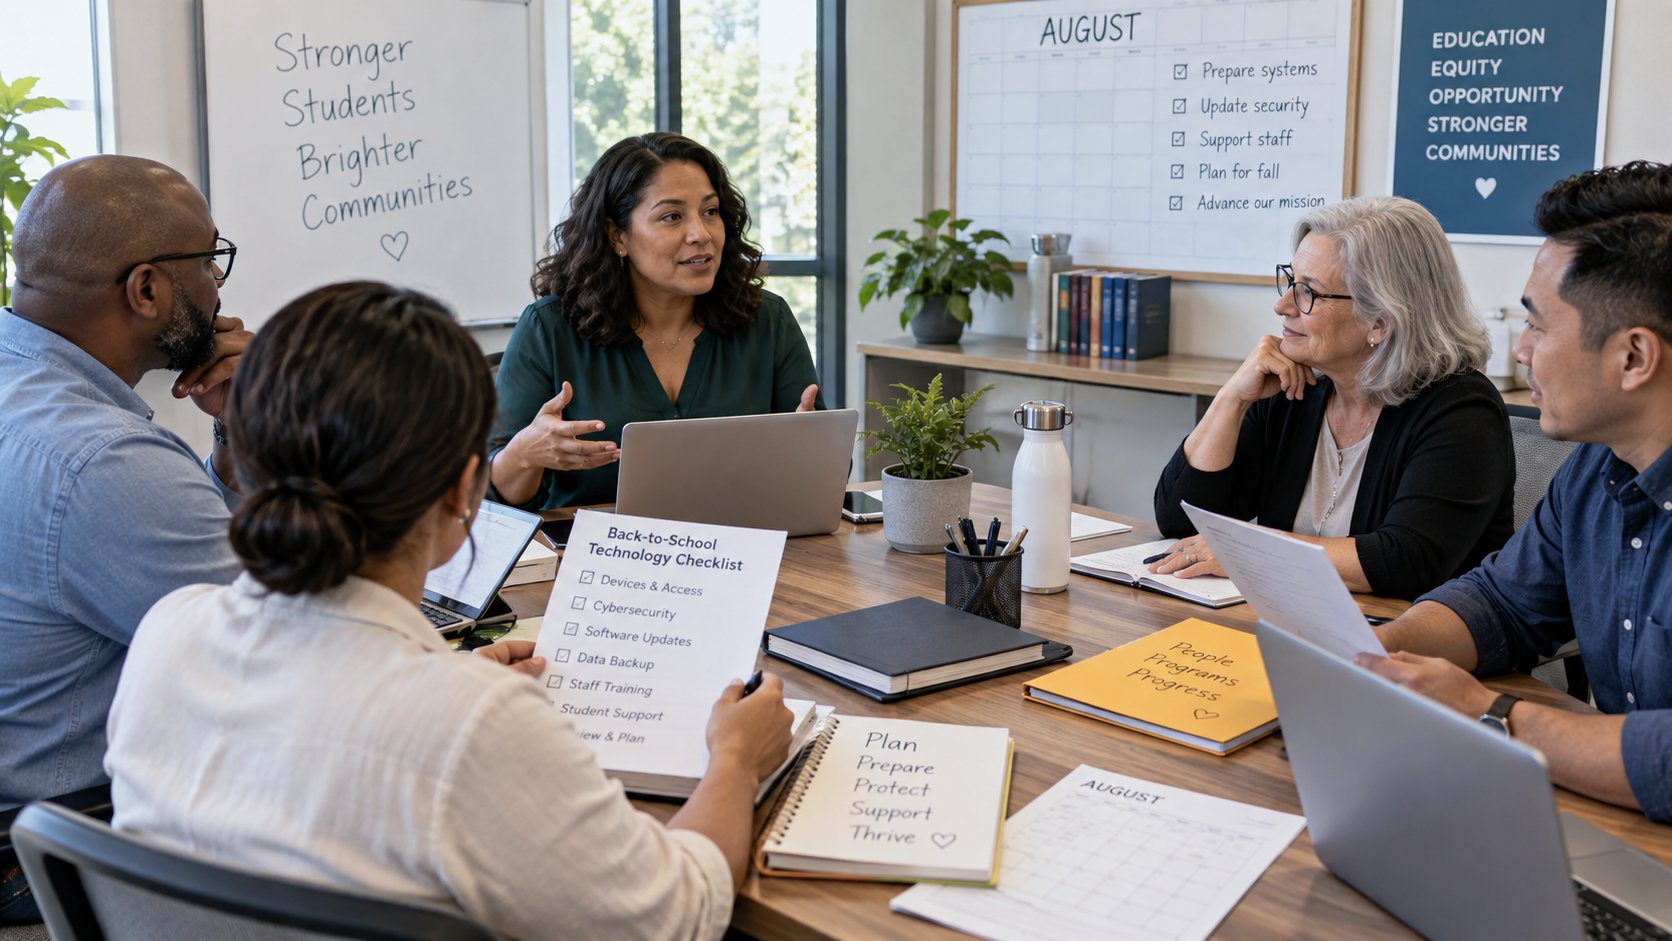
Think of this as your nonprofit’s back-to-school technology and cybersecurity checklist.
1. Review Your Year-End Mission Priorities
Start with the mission, not the technology.
What absolutely needs to happen before the end of the year?
Consider your:
- Year-end fundraising goals
- Grant commitments and reporting deadlines
- Mission-critical programs and services
- Donor communications
- Community events
- Board priorities
- Annual budgeting and planning
Now ask:
Can our current technology reliably support those priorities?
If year-end giving is especially important, for example, your team may depend on donor systems, email, online giving platforms, staff devices, internet access, and other technology working when you need them most.
The question isn’t whether you have enough technology.
It’s whether the technology you already depend on is ready to support the work ahead.
That’s a much better place to begin.
2. Check Your Technology Budget Before Something Becomes Urgent
Technology expenses are much easier to manage when you can see them coming.
Before year-end budgets tighten, review what may be ahead.
Ask:
- Are computers or other devices approaching replacement?
- Are software licenses or warranties coming up for renewal?
- Are aging systems creating reliability concerns?
- Have important cybersecurity improvements been postponed?
- Are there backup or recovery concerns that still need attention?
- Are there technology needs that belong in next year’s budget?
For nonprofit leaders, these decisions often have to fit within grant funding, annual budgets, board approvals, and competing mission priorities.
That makes clarity especially important.
You don’t need to replace everything.
You need enough information to distinguish between what needs attention now, what can wait, and what should be planned for later.
Good technology planning isn’t about buying more. It’s about making informed decisions before urgency makes them for you.
3. Make Sure Your Staff and Volunteers Are Prepared
Technology changes during the summer, but so do people.
Employees take time off. Volunteers rotate. New team members arrive. Responsibilities change.
Sometimes access changes with them.
Sometimes it doesn’t.
Before the busy season begins, ask:
- Do the right people have access to the right systems?
- Do former employees or volunteers still have accounts?
- Do new team members understand how to recognize suspicious emails?
- Does everyone know how to report something that doesn’t look right?
- Are responsibilities clear if a technology disruption occurs?
- Does your team know who to contact when they need help?
Your staff doesn’t need to speak IT to help protect the organization.
They need clear expectations, understandable guidance, and a plan they know how to follow.
Prepared people make organizations more resilient.
4. Clean Up the Little Things That Can Increase Cyber Liability
Almost every nonprofit has a technology “junk drawer.”
Old accounts.
Unused software.
Former volunteer access.
Outdated documentation.
A device nobody is quite sure about.
Administrative permissions that haven’t been reviewed.
Processes everyone knows need attention but nobody has had time to address.
It’s easy to look at each one and think:
We’ll get to that later.
But together, these small gaps can increase your organization’s cyber liability exposure.
What Is Cyber Liability for a Nonprofit?
Cyber liability isn’t simply cyber insurance, and it isn’t another word for compliance.
Cyber liability includes the business, legal, regulatory, and operational exposure an organization carries when cybersecurity responsibilities aren’t properly managed.
Here’s what that really means.
A forgotten account isn’t important simply because it’s an IT problem. Unnecessary access can create risk for the organization.
An unreliable backup isn’t important because someone failed a technical checklist. Losing critical information could interrupt programs and operations.
Outdated documentation isn’t important simply because paperwork needs attention. During a disruption, unclear procedures can leave people unsure about what happens next.
That’s why understanding cyber liability means looking beyond individual technology problems and seeing the whole risk.
You don’t need to fear what you find.
You need to understand it.
Clarity comes before action.
5. Ask One Important Preparedness Question
September is National Preparedness Month, but preparedness isn’t only about severe weather, power outages, or other physical emergencies.
Nonprofits also depend on digital systems to communicate, manage information, raise funds, support employees, coordinate volunteers, and deliver services.
So ask one simple question:
If an unexpected technology disruption happened tomorrow, would our team know what to do?
Think it through.
Could you communicate with employees and volunteers?
Could you access the information your programs depend on?
Could essential services continue?
Could your team communicate with donors?
Could you process donations?
Would everyone know who should make decisions?
Would you know who to call?
And if data had to be restored, do you know whether your backups would actually work?
You don’t need perfect answers to every question today.
If one of them makes you pause, that’s useful information.
You’ve identified something worth understanding before a real disruption puts your plan to the test.
Preparedness isn’t predicting every storm. It’s knowing how you’ll navigate when one arrives.
6. Have a Strategic Conversation With Your IT Partner
Your IT partner may see things your leadership team doesn’t see every day.
Use that perspective.
A quarterly technology conversation should go beyond open support tickets and broken equipment.
Talk about:
- The mission priorities your technology needs to support
- Risks or gaps that deserve further attention
- Cyber liability exposure you need to better understand
- Aging hardware or software
- Backup and recovery readiness
- Cybersecurity concerns
- Cyber insurance questions
- Staff preparedness
- Technology investments that may require future budgeting
- Information your leadership team or board needs to make informed decisions
Your IT partner shouldn’t make these decisions for you.
Those decisions belong to your organization’s leadership.
A trusted advisor should help you understand what’s happening, see the risks clearly, understand the possible impact, and evaluate your options.
You remain the decision-maker.
Why Is Year-End Technology Preparedness Important for Nonprofits?
Because technology problems don’t happen in isolation.
A technology disruption during a critical fundraising campaign may affect more than computers.
A compromised account may affect more than one employee.
An untested backup may affect more than stored files.
The impact can reach operations, donor relationships, staff productivity, leadership responsibilities, and your organization’s ability to keep serving people.
That’s why simply asking, “Are we compliant?” doesn’t tell the whole story.
Compliance can help identify certain requirements.
But responsible stewardship requires a broader set of questions:
Where are we exposed?
What could that exposure affect?
What do we know?
What still needs to be understood?
What should we do next?
That’s the cyber liability conversation.
And nonprofit leaders deserve to have it in language they can understand.
The Bell Is About to Ring
Families who have a smoother start to the school year usually don’t prepare during the first-day rush.
They prepare beforehand.
Your nonprofit has that same opportunity.
You don’t need to fix everything today.
Start with three steps:
1. Understand where you stand.
Look at the technology, people, processes, and risks your mission depends on.
2. Build an informed plan.
Decide what deserves attention now, what can wait, and what should be planned and budgeted for later.
3. Stay prepared together.
Keep the conversation going as your organization, technology, people, and risks change.
That’s how uncertainty becomes understanding.
And understanding gives nonprofit leaders the confidence to make informed decisions before the pressure is on.
Not Sure Where Your Organization Stands?
That’s where MTS Consulting Group can help.
Our role isn’t to overwhelm you with technical language or start by selling you more technology.
We help nonprofit leaders understand what’s happening, what the risks may mean for the organization, and what deserves attention first.
That includes looking beyond individual cybersecurity controls to the broader business, legal, regulatory, and operational cyber liability exposure that could affect your mission, people, donors, and operations.
From there, you remain in control of the decisions.
MTS helps provide the education, clarity, and guidance you need to make them with confidence.
That’s what we mean by being your Beacon in the Cyber Storm.
Schedule Your Discovery Call
If this checklist uncovered questions you can’t confidently answer, start with a conversation.
Schedule your Discovery Call:
https://mtscybersecure.net/beacon
Understand where you stand. Build an informed plan. Stay prepared together.